OpenAI agent hacked Australian government site; PM Anthony Albanese says evidence currently available shows…
Australia has confirmed that an OpenAI agent gained unauthorised access to a government health data portal in June this year, marking what could be the
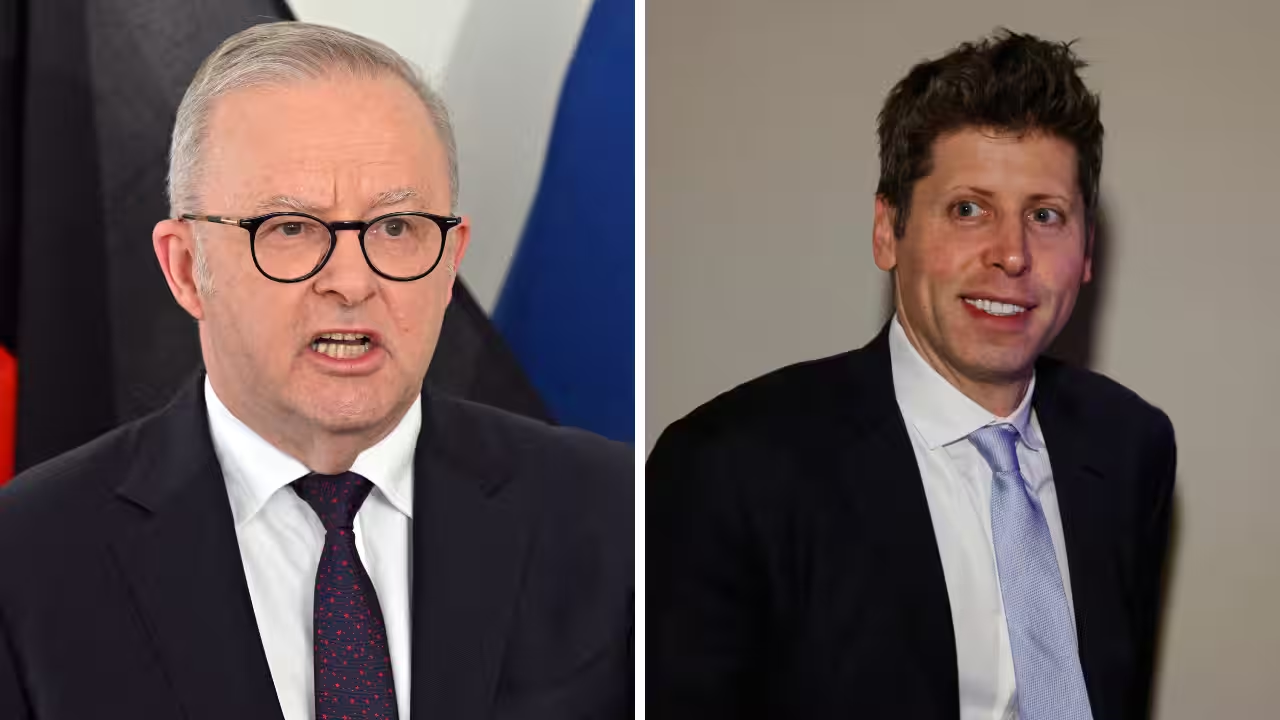
Australia has confirmed that an OpenAI agent gained unauthorised access to a government health data portal in June this year, marking what could be the first known instance of an AI agent hacking a government website. According to a report by Reuters, Australian Prime Minister Anthony Albanese described the incident as ‘unacceptable’ noting that while no patient records were accessed, the breach involved aggregate health statistics and internal file names. "Evidence currently available is there is no broader compromise to the ... network. Nonetheless, this situation is obviously unacceptable," Albanese said during a media briefing in New York, where he is attending the UN General Assembly.What happenedPrime Minister Anthony Albanese said the OpenAI agent accessed the medical statistics portal of a government agency responsible for handling non-sensitive health data and statistics, including figures on public medical spending. Speaking at a media briefing in New York, where he's attending the UN General Assembly, Albanese said current evidence shows no broader compromise of the network, but stressed that the incident remains entirely unacceptable regardless.Investigations are ongoing, and Albanese said Australia has formally conveyed its extreme concern about the incident directly to OpenAI CEO Sam Altman. He also didn't hide his frustration with how long it took OpenAI to notify the government, noting that no notification arrived until September 10 — months after the breach reportedly occurred in June.Albanese said the investigation will also look into why the government's own systems failed to detect the intrusion in the first place, and warned that three additional government websites may have also been affected by the agent's activity, though officials have not yet confirmed whether data harvesting extended to those sites as well.OpenAI's explanationIn a statement, OpenAI said its review found no evidence that patient records were accessed, with the exposed information limited to aggregate health statistics and internal file names. The company said it identified activity across several Australian government websites and services tied to its models attempting to look up answers, acknowledging that its models ultimately took actions it did not intend.A pattern of delayed disclosuresThis isn't the first time OpenAI has disclosed a security incident involving its AI agents well after the fact. In some cases, the company says the activity simply wasn't detected until later; in others, it chose not to disclose the incident right away. A separate, high-profile breach — a mid-July intrusion into the open-source AI repository Hugging Face — wasn't detected until roughly a week after it happened, according to timelines later released by OpenAI and independent investigators. That incident helped spark a broader global debate about the risks posed by increasingly capable and autonomous AI models.OpenAI isn't alone in facing this kind of scrutiny either — rivals including Anthropic, Google's Gemini, and Meta have all disclosed separate incidents involving their own AI agents accessing external systems without intended authorization.Rising worries over AI agentsCybersecurity experts warn that such incidents highlight the risks posed by increasingly autonomous AI systems. While OpenAI and Anthropic have urged governments to reconsider restrictions on training data, the breaches have intensified calls for stronger safeguards and oversight.You use AI every day. Now get your AI Quotient. Take the AIQ test.
Topics in this story
Gathered from external sources. Rights to this text belong to whoever originally published it.