‘I have not seen anything like this in a long, long time,’ Microsoft CEO Satya Nadella as companies, governments rush to patch PHP flaws
As global corporations and government agencies scrambled to patch critical, newly uncovered vulnerabilities in PHP – the foundational programming language
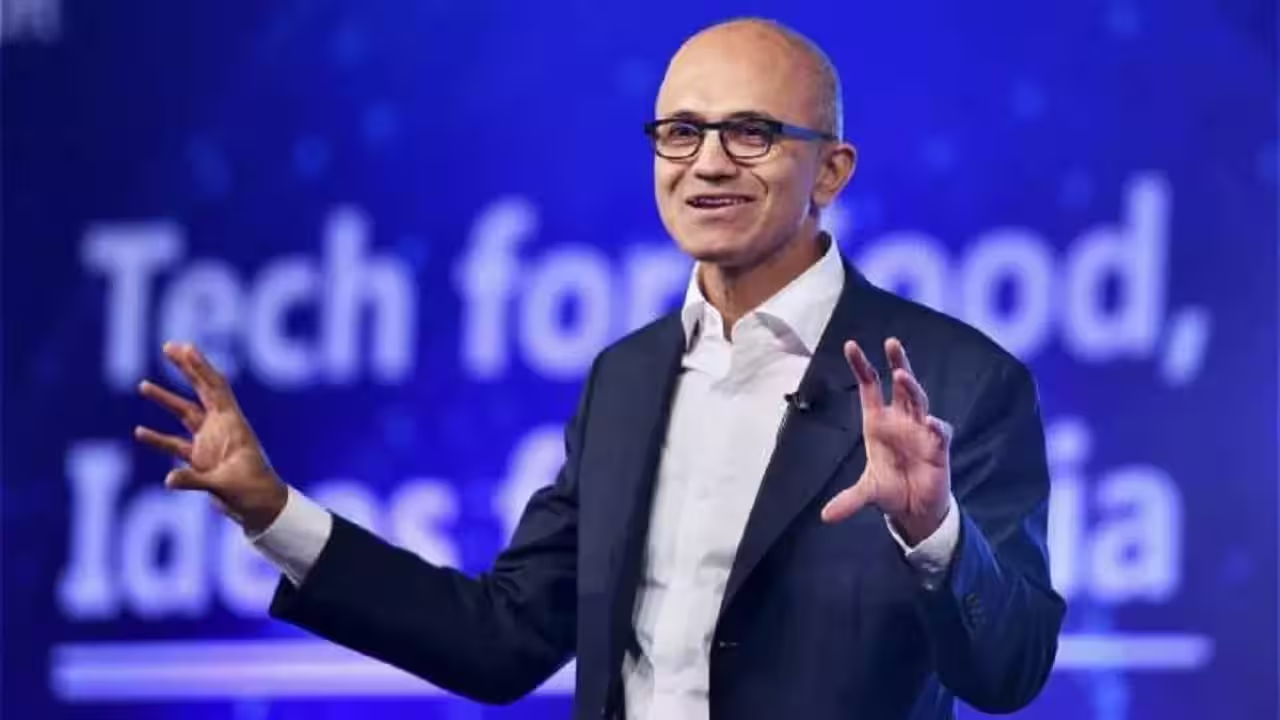
As global corporations and government agencies scrambled to patch critical, newly uncovered vulnerabilities in PHP – the foundational programming language that powers a majority of the worldwide web – top technology executives, including Microsoft CEO Satya Nadella, reacted to the unfolding crisis during an industry event in Germany this week. This comment came as security firms recorded millions of automated exploitation attempts within hours of the bug’s public disclosure.“I’ve not seen anything like this in a long, long time. It was a long day and a long night, I know, for all the IT and security folks,” Nadella said, stressing that the incident highlights how vital it is to build maintainable, secure software as architectures grow exponentially complex, as per news agency Reuters.Government and public websites go darkFrom Tokyo to Helsinki, emergency shutdowns hit banking portals, rail services, flight bookings, tax departments and municipal communications – triggering one of the most severe real-world stress tests ever faced by the aging, open-source codebases that keep people online.PHP operates as an essential web-building block alongside fundamental standards like HTML and Python. On Wednesday (October 21), the core development team behind PHP published emergency security patches for flaws that had sat undetected within the code for years before being brought to light using artificial intelligence. The team urged users across the globe to “update immediately.”However, the timing of the release created severe exposure. Madeline Lawrence, co-founder of Belgian cybersecurity firm Aikido Security, noted that technical details surrounding the bugs entered the public domain before organizations were ready with deployed patches, triggering immediate exploitation.“Companies are racing to update against attackers who can use AI to exploit them. That’s the whole race,” Lawrence said. The scale of the threat was confirmed by network performance and security provider Cloudflare, which tracked an immediate, exponential surge in automated intrusions hitting its global infrastructure.Posting on X (formerly Twitter), Cloudflare CEO Matthew Prince broke down the staggering timeline:10 Hours Prior to Public Disclosure: Thousands of probing attempts were logged across the network.45 Minutes Post-Announcement: Attack volumes jumped to tens of thousands.2 Hours Post-Announcement: Exploitation attempts escalated into hundreds of thousands.Current Volume: Sustained attack runs have surged into the millions.Fearing catastrophic data compromises, dozens of major corporations and state ministries chose to sever public access entirely while engineers raced to deploy patches. Prominent corporate names suspended major online operations in Japan, Europe (France, Finland) and Asia (China and South Korea).You use AI every day. Now get your AI Quotient. Take the AIQ test.
Topics in this story
Gathered from external sources. Rights to this text belong to whoever originally published it.